Cyber Security

CISA Adds 5 Actively Exploited Artifactory, ScreenConnect, and RouterOS Flaws to KEV

î „Ravie Lakshmananî ‚Sep 12, 2026Vulnerability / Enterprise Security The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has identified five security vulnerabilities affecting JFrog Artifactory, ConnectWise ScreenConnect, and MikroTik RouterOS. These vulnerabilities have been actively exploited in the wild, prompting CISA to …

CISA Adds 5 Actively Exploited Artifactory, ScreenConnect, and RouterOS Flaws to KEV Read More »

SpyCloud 2026 Identity Threat Report Finds Non-Human Identities Are Now the Leading Path into the Enterprise – Latest Hacking News

164 Austin, Texas / USA, September 9th, 2026, CyberNewswire Ninety-five percent of organizations believe they have visibility into their AI and machine identity exposures, yet only 36% are actually monitoring them. SpyCloud, the leader in identity threat protection, today released …

SpyCloud 2026 Identity Threat Report Finds Non-Human Identities Are Now the Leading Path into the Enterprise – Latest Hacking News Read More »

Reflectiz Launches Agentic Pentesting for Websites: Up to 10x Coverage vs Conventional Pentests – Latest Hacking News

62 Boston, MA, USA, September 8th, 2026, CyberNewswire Specialized team of AI agents that discover, attack, and validate web vulnerabilities, leveraging pre-existing site context to eliminate noise and speed remediation.  Reflectiz, the continuous web exposure management company, today launched a …

Reflectiz Launches Agentic Pentesting for Websites: Up to 10x Coverage vs Conventional Pentests – Latest Hacking News Read More »

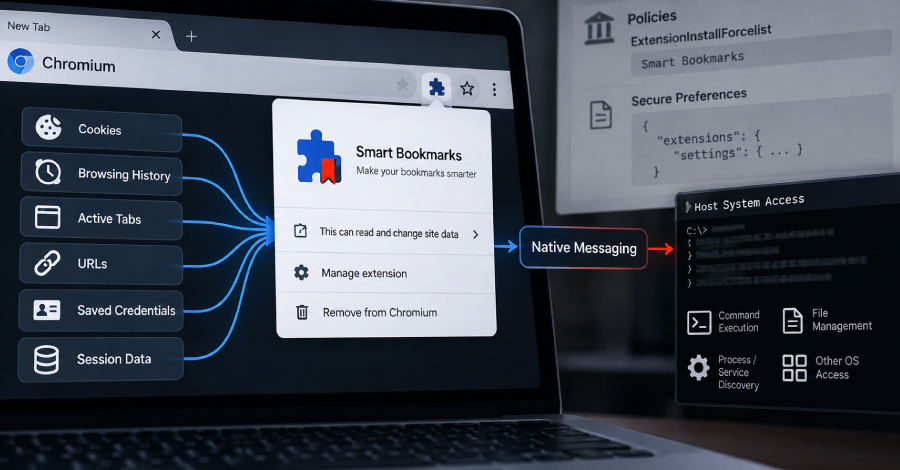
PEEP Turns Chrome and Edge Into Post-Compromise Backdoors for Host Command Execution

Cybersecurity experts have recently exposed a sophisticated Chromium-based post-exploitation toolkit known as PEEP, posing as a bookmarks extension for web browsers. Requiring prior administrative or code execution access, PEEP’s installer injects the extension directly into Chrome/Edge profiles, bypassing Web Store …

PEEP Turns Chrome and Edge Into Post-Compromise Backdoors for Host Command Execution Read More »

Attackers Hijack MikroTik Routers Through Internet-Exposed SSH Without Authentication

î „Swati Khandelwalî ‚Sep 06, 2026Vulnerability / Network Security Recent reports indicate that attackers are taking advantage of vulnerabilities in MikroTik routers, specifically targeting the Secure Shell (SSH) remote-access service. This exploit allows unauthorized access without the need for authentication, as highlighted …

Attackers Hijack MikroTik Routers Through Internet-Exposed SSH Without Authentication Read More »